
Zürich, Switzerland · on Azure since 2019
I build Azure infrastructure that survives production.
This is where I write down what happened after the deployment — the patterns that held up, the things that broke, and the tools I built along the way.
Terraform & IaCEntra IDPowerShellGovernance
31Articles
12Tools
- RoleCloud Engineer, enterprise Azure
- CertifiedAZ-104 · GPCS
- FocusIaC · Identity · Governance
- Status● Open to chat
Latest article
Fresh out of production.
The VMs that LAPS cannot reach still have passwords
Read article →: The VMs that LAPS cannot reach still have passwordsWindows LAPS handles domain-joined machines. Entra login removes the local credential entirely. This is about the machines neither one reaches, and a tool that rotates their passwords and SSH keys off a…
From the blog
Recently written.
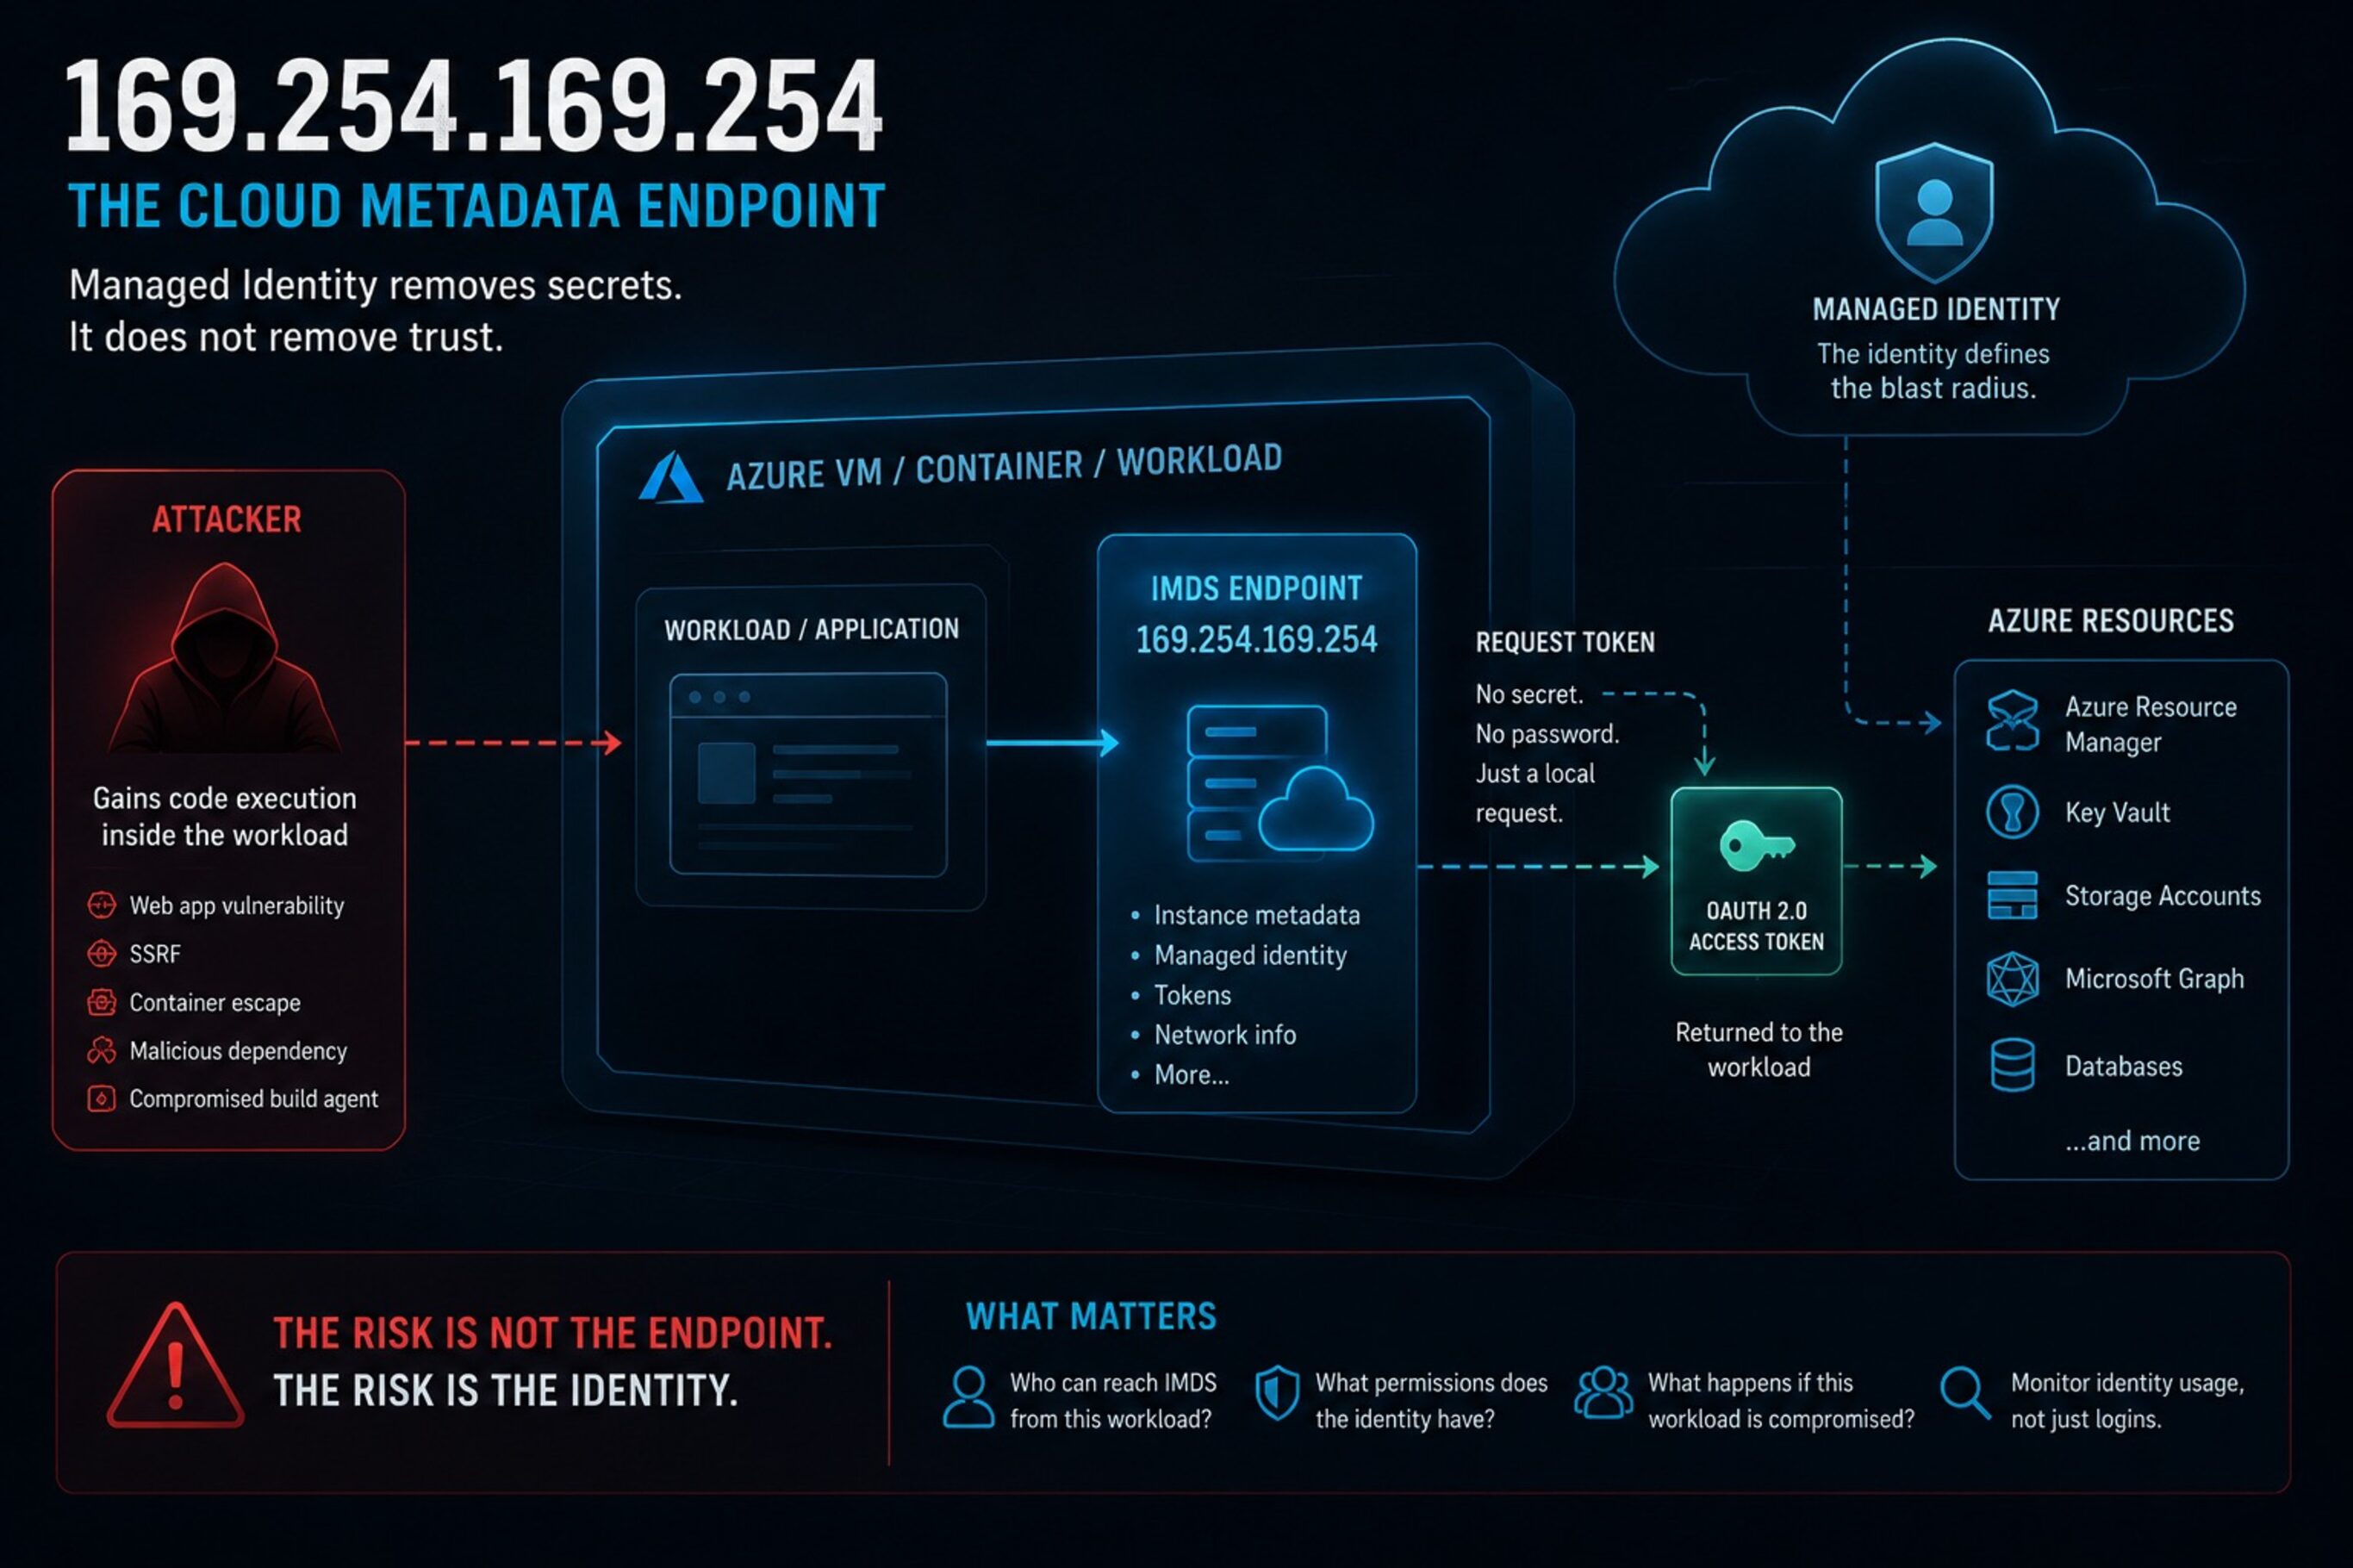
169.254.169.254: The Cloud Metadata Endpoint
Managed Identity solves credential storage problems. It does not eliminate identity abuse. Managed Identity is one of those Azure features almost everyone recommends — and honestly,…azureknowledgesecurity
There’s no built-in policy for Entra VM login
Azure ships a built-in policy to disable local accounts on your VMs. It ships none to enable the Entra login that makes disabling them survivable. Here’s…azureentraidWhat I work on
Six things I go deep on.
Not one hub per tag — these are the areas where the writing actually stacks up into something you can work through.
Terraform & IaC on Azure
Modules, state, secrets and the file layout that survives a second engineer. Terraform first, ARM and Bicep where they still win.Entra ID & Least Privilege
Almost every Azure environment grants more than it can justify, because Contributor was faster than reading the role definitions. This is about getting the permissions right and keeping them right.Azure Automation & PowerShell
Work that should not need a human: runbooks, Logic Apps, Functions and the scripts that make a request turn into a machine.Azure Governance & Compliance
Proving the tenant is in the state you claim it is: policy, logging, agents and the audits that find what nobody deployed on purpose.Azure Landing Zones
Structure a subscription estate before it structures itself: management groups, network design and the platform decisions that are expensive to reverse.Azure Cost Optimization
Machines that switch themselves off, and the spend nobody signed off on. Mostly tagging, schedules and the gap between stopped and deallocated.Things I build
Tools & projects.
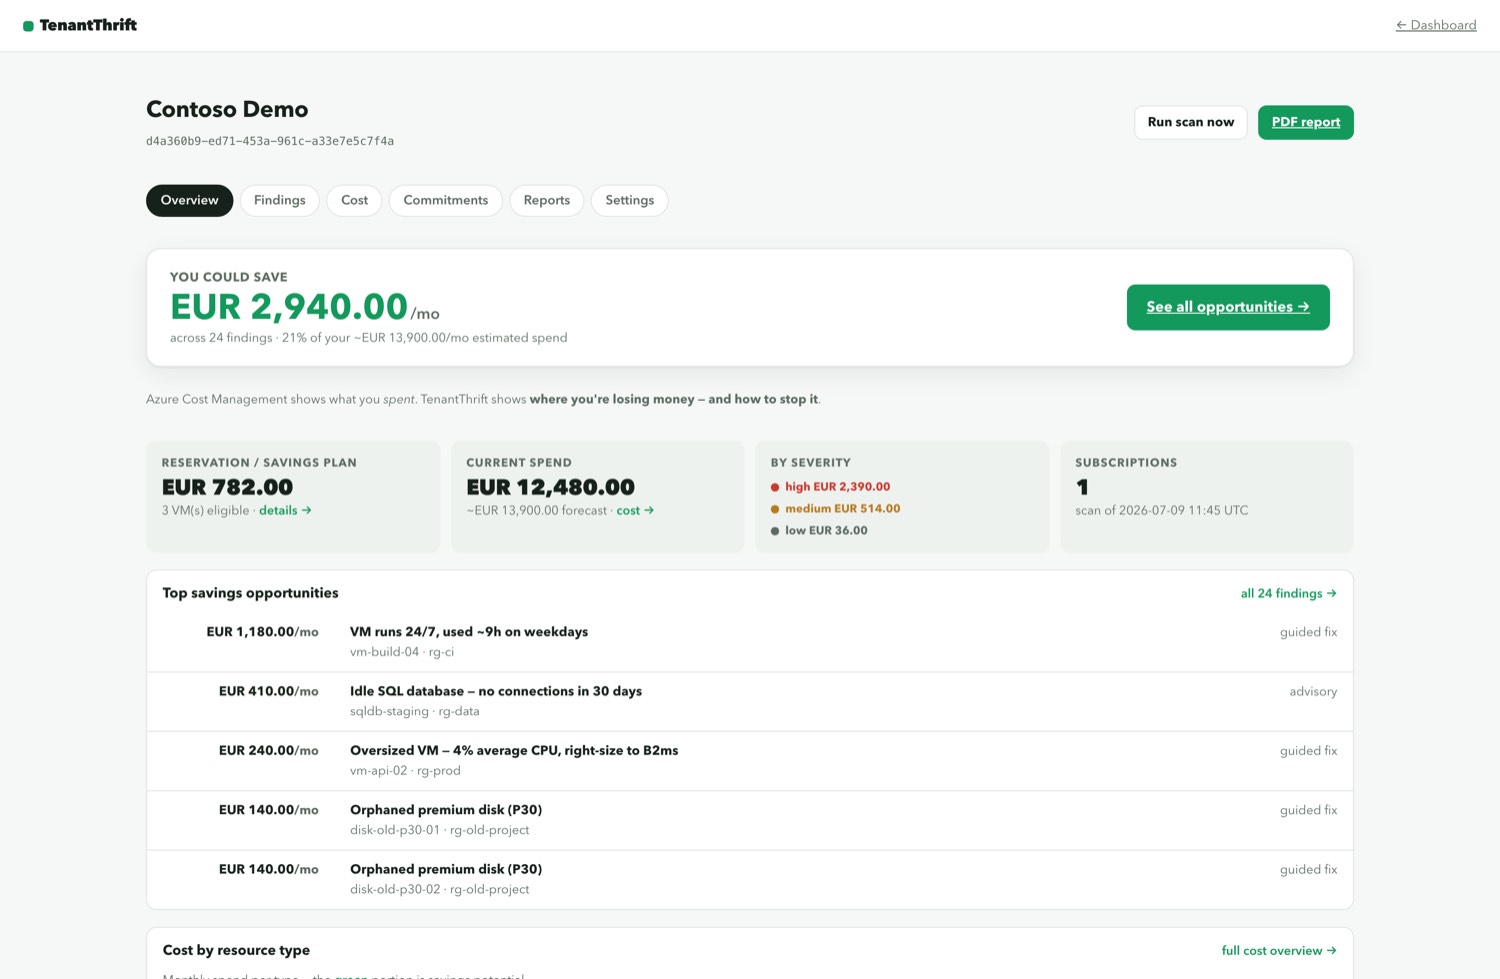
TenantThrift
● LiveProductFinds the Azure spend nobody signed off on — idle, oversized and orphaned resources, each with a euro amount and a guided fix.
14-day trial
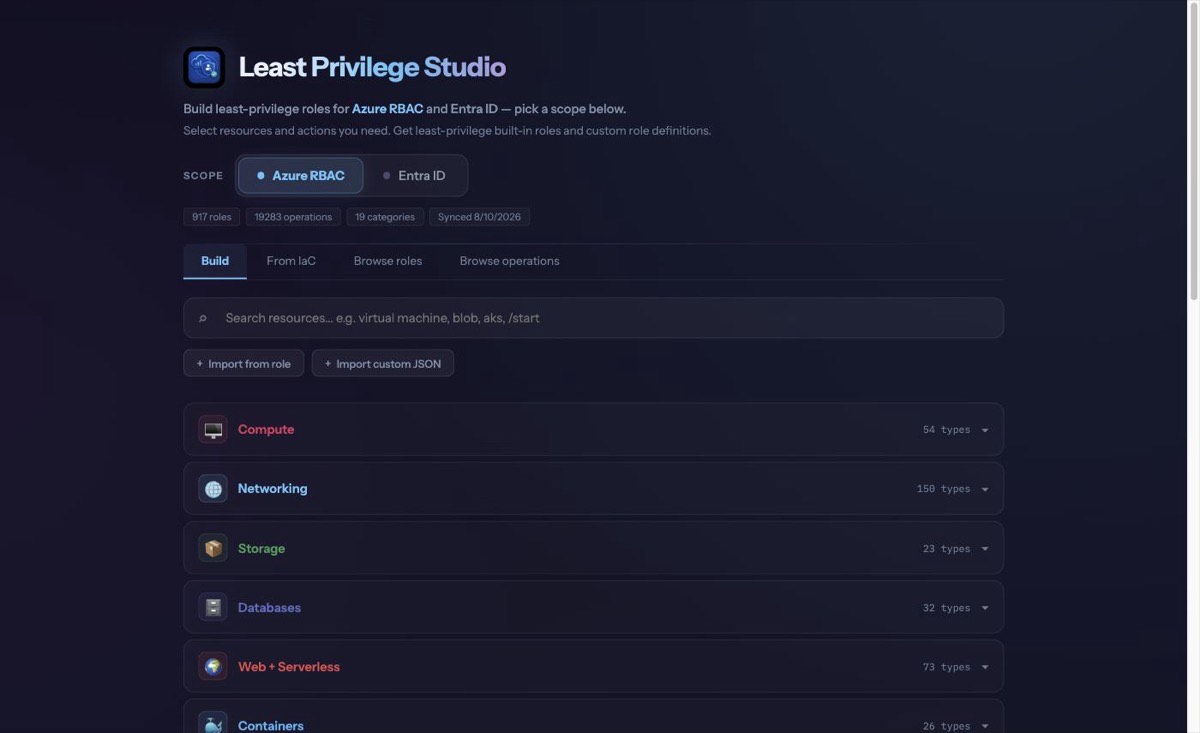
Least Privilege Studio
● LiveFreePick the actions you need for Azure RBAC or Entra ID and get the narrowest roles that cover them — or just paste in your Terraform.
no login
Plus 4 scanners, 4 automations and 2 blueprints. See all tools →
About me
Cloud engineer in Zürich. Most of what’s here came from problems I had to solve at work.
Where the documentation ran out and I had to figure things out the hard way. If something here saved you a few hours, that’s the whole point.